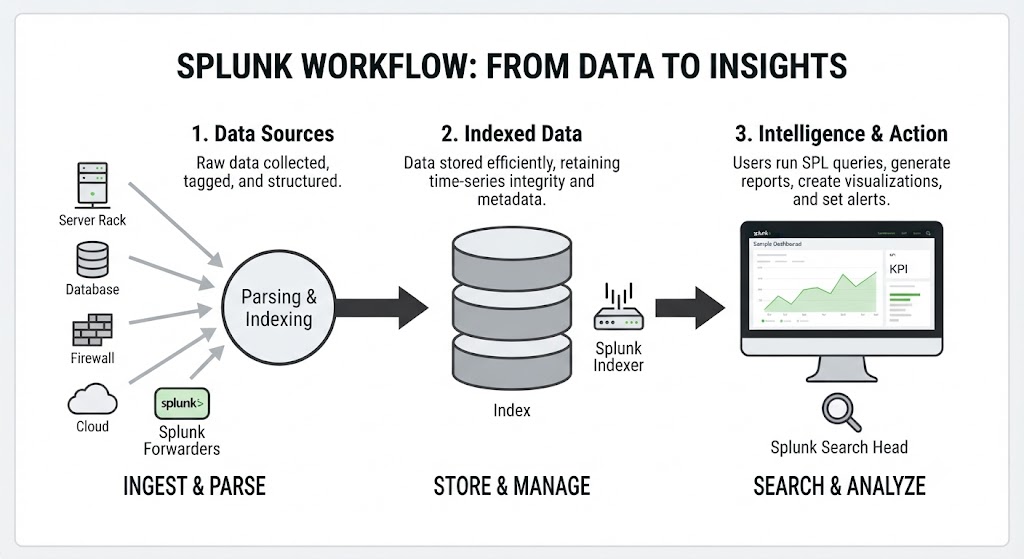
Splunk Explained: From Raw Machine Data to Searchable Insights
A practical and informative guide to Splunk covering data ingestion, forwarders, indexers, search heads, SPL, field extraction, dashboards, alerts, SIEM workflows, troubleshooting and real-world academic projects.